Cyber Threat Monitoring
Collects security events from enterprise systems, classifies threats by severity/category, and correlates incidents across multiple data sources.
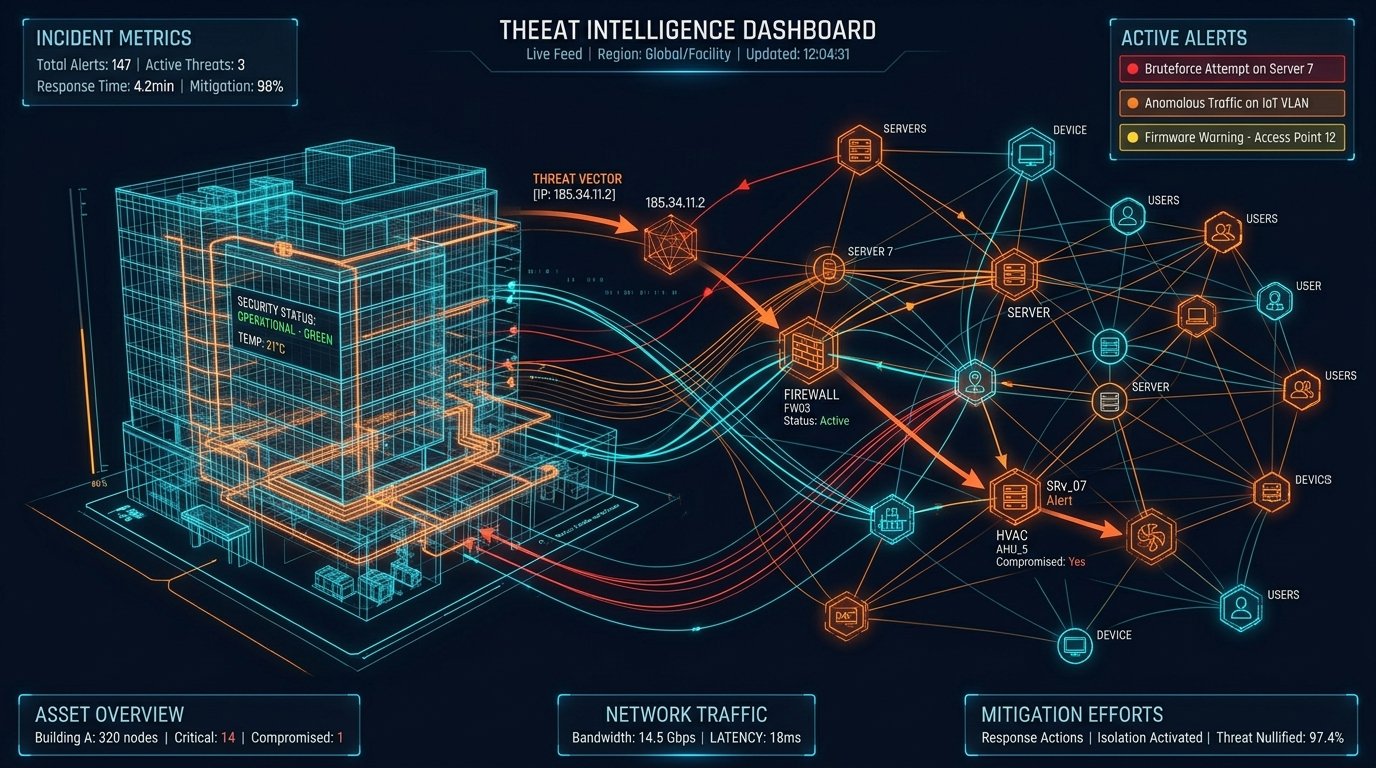
Built for high-consequence enterprise operations.
High-Throughput Enterprise Log Ingestion
Ingests syslog, audit streams, network flows, and cloud API events with sub-second latency. Connects seamlessly with standard enterprise infrastructure, firewalls, and endpoint detection agents without performance degradation.
MITRE ATT&CK Mapping & Threat Classification
Automatically tags every detected threat against the MITRE ATT&CK taxonomy, categorizing attacks by tactic, technique, and severity. Enables security teams to rapidly understand attack vectors and adversary intentions.
Cross-Domain Event Correlation Engine
Correlates raw cyber telemetry against physical access logs and authentication histories using Complex Event Processing (CEP). Identifies stealthy anomalies such as impossible physical travel and compromised privileged credentials.
Who operates Cyber Threat Monitoring and how it transforms response.
Designated Operators
Automates threat classification and correlation so analysts focus on high-impact containment rather than manual log parsing.
A Day in the Life
"IT administrators and cyber analysts review threat streams where network anomalies are pre-correlated with employee location data, stopping credential hijacking before lateral movement occurs."
Works better together with adjacent engines.
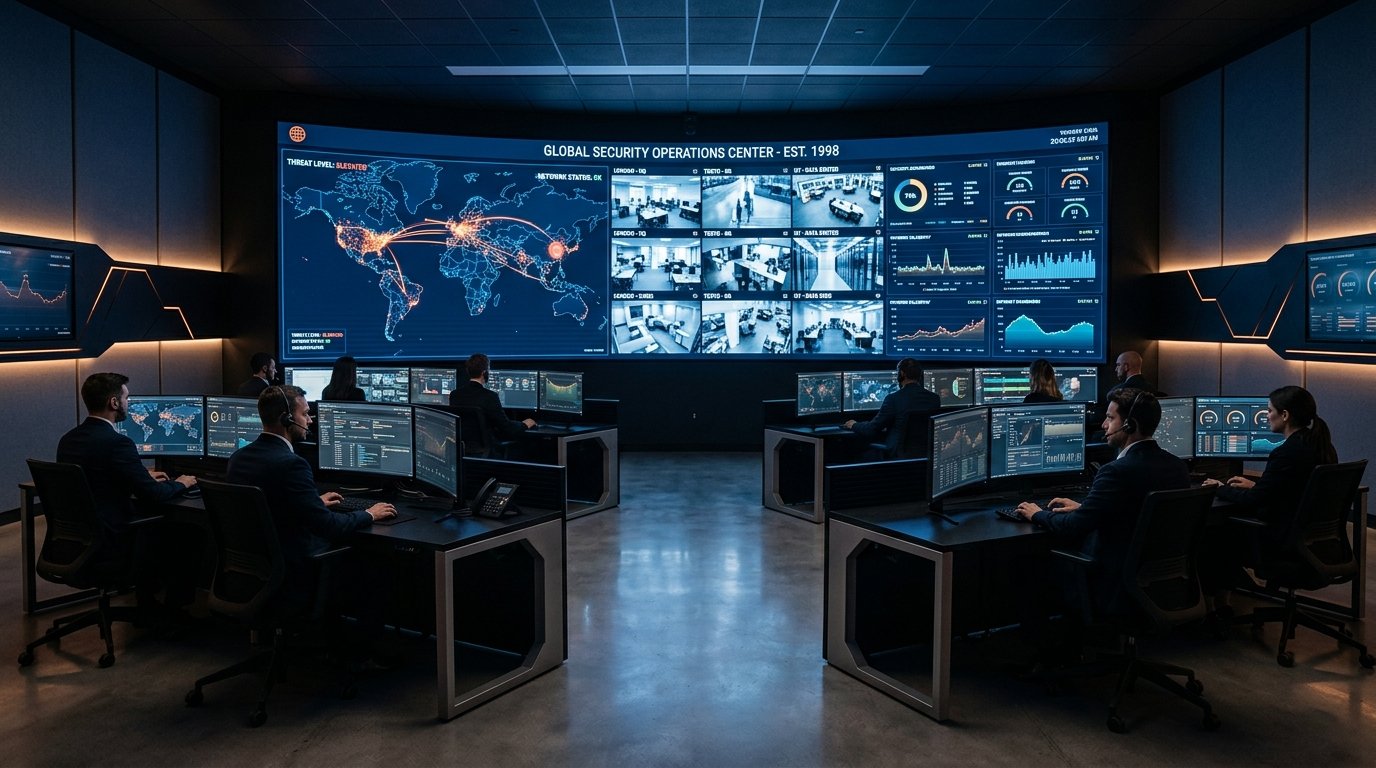
SOC Dashboard
Centralized, real-time view of every security event, active threats, incidents, alarms, and live asset health across digital and physical perimeters.
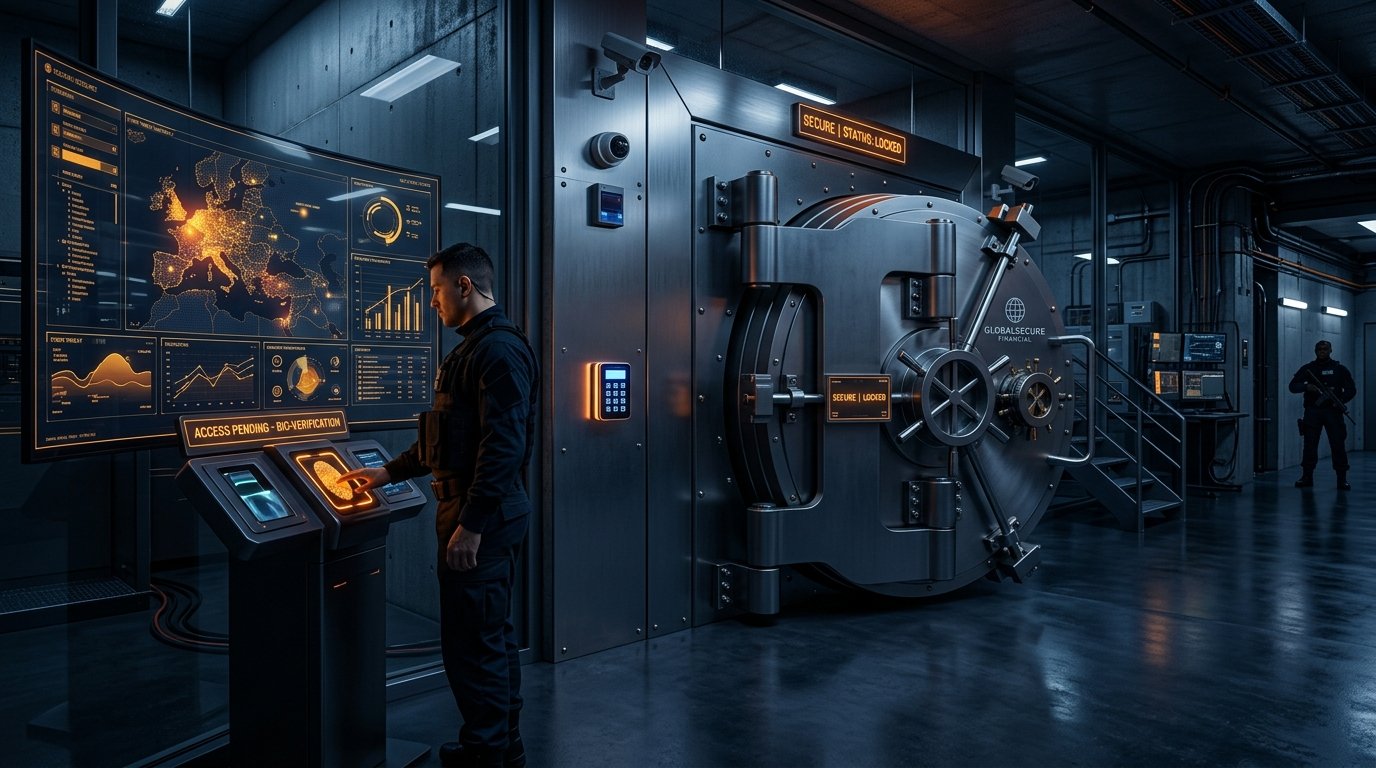
Identity & Access Control
Manages employee/contractor identities, assigns access by department and security level, and logs all entry/exit activity with immutable audit trails.
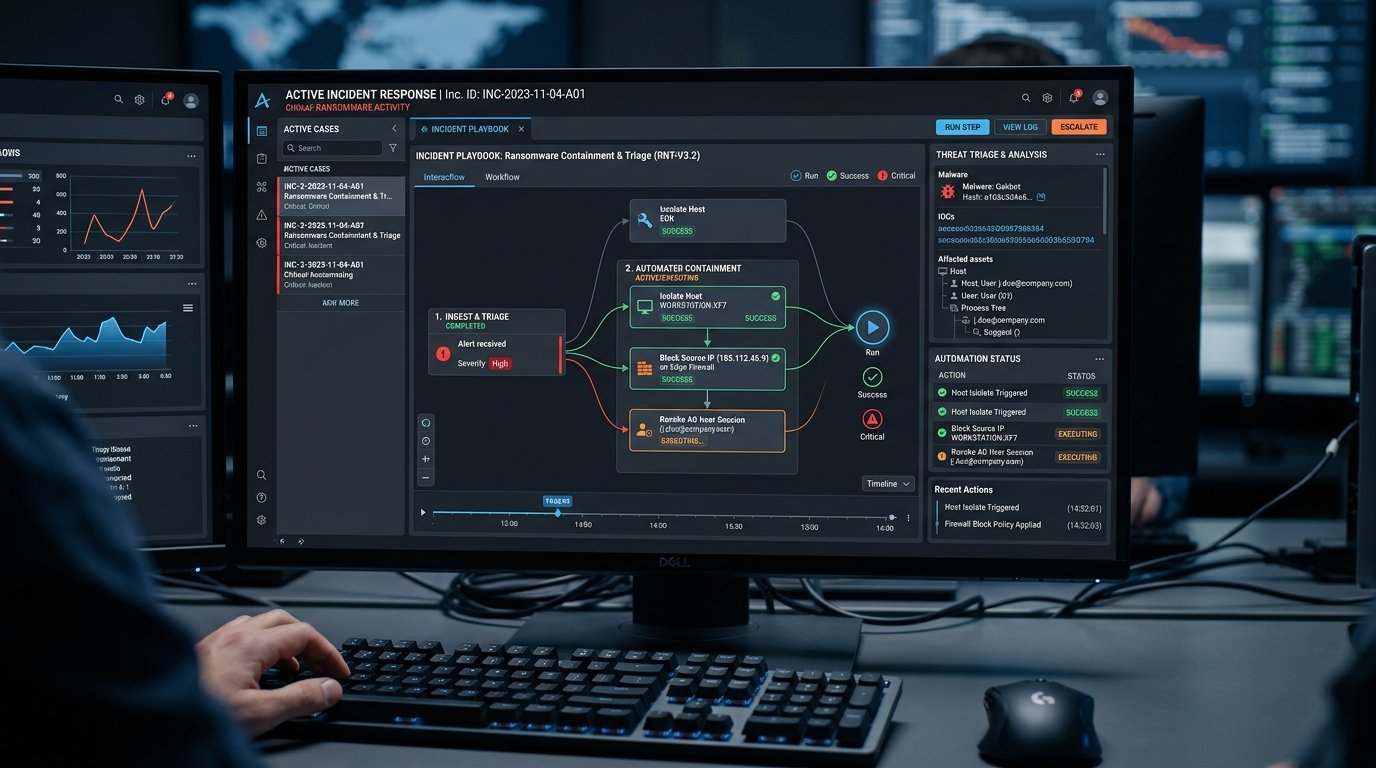
Incident Response Management
Create, assign, investigate, and resolve incidents; evidence collection, root-cause analysis, corrective actions, and configurable escalation.
See Cyber Threat Monitoring in action.
Experience how Cyber Threat Monitoring integrates seamlessly with your existing infrastructure and the rest of the RedFort platform.