One command center for every security signal cyber, physical, and compliance.
RedFort unifies SOC monitoring, physical access control, CCTV systems, and incident response into a single operational dashboard — so nothing falls into a blind spot.
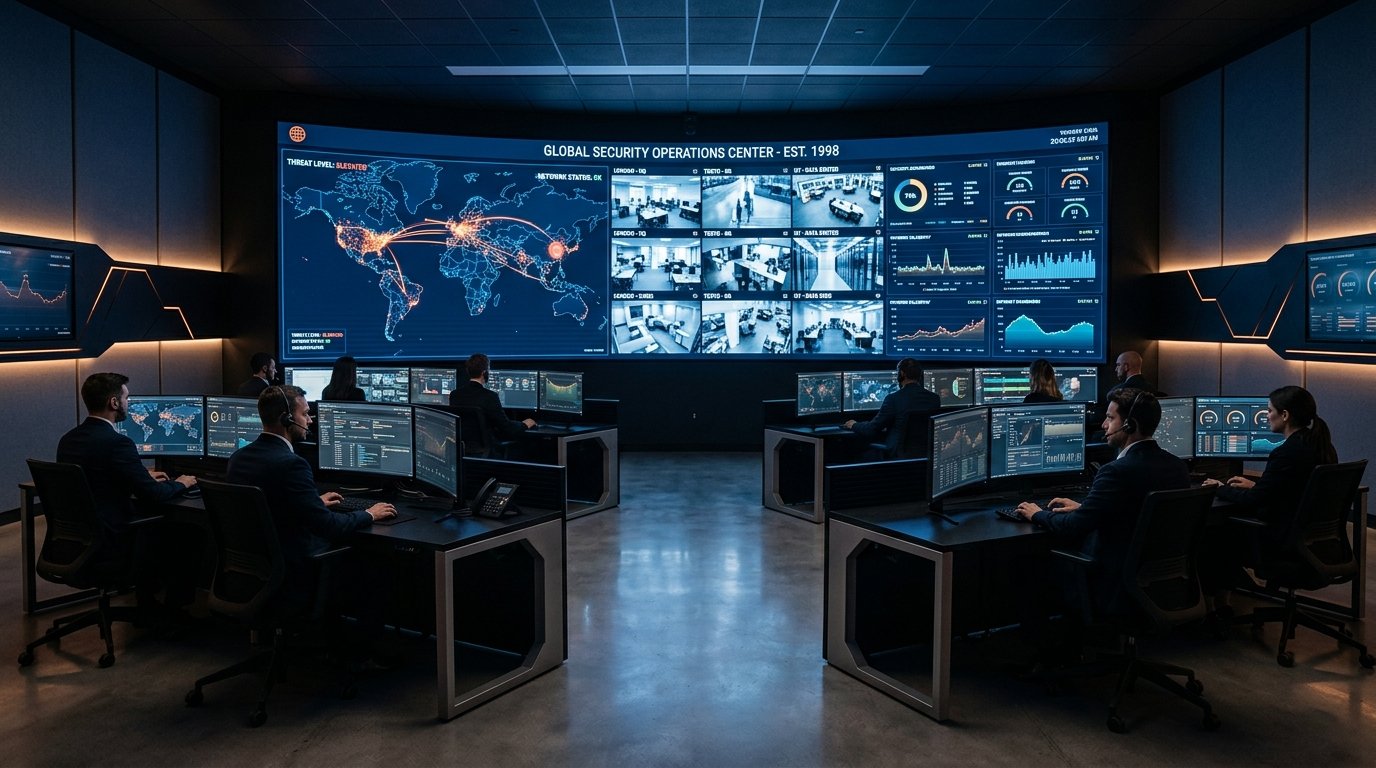
Global Security Operations Center
Unified real-time monitoring across distributed data centers, enterprise campuses, and cloud infrastructure.
The Multi-Vector Blind Spot
When cyber SIEM, physical PACS, and compliance tools run in silos, cross-domain threats bypass detection. RedFort correlates every signal with sub-second precision.
The three pillars of unified enterprise defense.
Engineered for global enterprises to ingest millions of cross-domain events, execute sub-second containment playbooks, and automate continuous board-level governance.
Unified Signal Ingestion
Ingests cyber logs, physical badge swipes, RTSP CCTV feeds, and IoT sensors into one normalized event stream.
Autonomous SOAR Response
Executes dual-domain response playbooks instantly to isolate hosts, lock physical perimeters, and notify responders.
Actionable Risk Intelligence
Translates millions of low-level logs into continuous compliance postures and board-ready risk dashboards.
Tailored capabilities for every domain of enterprise security.
Unified SOC Monitoring Across Cyber Infrastructure and Physical Perimeters
"Before RedFort, our SOC analysts were constantly context-switching across four disconnected tools. Unifying cyber telemetry with physical alarms reduced our critical triage response time from 45 minutes to 38 seconds."
Nine modules. One unified platform.
SOC Dashboard
Centralized, real-time view of every security event, active threats, incidents, alarms, and live asset health across digital and physical perimeters.
Cyber Threat Monitoring
Collects security events from enterprise systems, classifies threats by severity/category, and correlates incidents across multiple data sources.
Physical Security Management
Manages buildings, entry points, CCTV systems, alarms, and checkpoints; monitors visitor access; and records and investigates physical incidents.
Identity & Access Control
Manages employee/contractor identities, assigns access by department and security level, and logs all entry/exit activity with immutable audit trails.
Incident Response Management
Create, assign, investigate, and resolve incidents; evidence collection, root-cause analysis, corrective actions, and configurable escalation.
Risk & Vulnerability Management
Identifies operational, cyber, and physical security risks, auto-calculates risk scores, and supports remediation planning.
Compliance & Audit Management
Manages compliance requirements and audits; findings generate corrective actions; and audit reports support regulatory inspection.
Security Analytics & Intelligence
Dashboards for security posture, incident trends, risk exposure, response time, compliance scores, and historical data for strategic planning.
Emergency Alerts & Notifications
Alerts for incidents, unauthorized access, cyber threats, and emergencies; multi-level escalation workflows; and instant emergency broadcast.
RedFort Platform — Govern the entire security program from one system
Register offices, configure hierarchies, establish multi-tier clearance zones, and enforce zero-trust security policies across your global enterprise.
Built for every stakeholder in the security lifecycle.
Granular role-based views ensuring executives, analysts, field guards, auditors, and employees get exact situational context.
Holistic posture metrics, enterprise risk exposure heatmaps, and board-level compliance ROI.
Correlated multi-vector threat feeds, guided SOAR investigation playbooks, and asset health telemetry.
Mobile checkpoint badge verification, live CCTV alarm streams, and instant panic dispatches with floorplan routing.
Read-only access to immutable audit logs, regulatory checklists, and one-click evidence package exports.
Digital NFC smartphone access badge, visitor self-service invites, emergency lockdown broadcasts, and evacuation muster safety check-ins.
Built on end-to-end encryption, multi-factor authentication, role-based access control, and immutable audit logs.
Fortify every asset. Secure every operation.
Join leading enterprise security teams consolidating cyber defense, physical PACS, and compliance into a single operational command center.